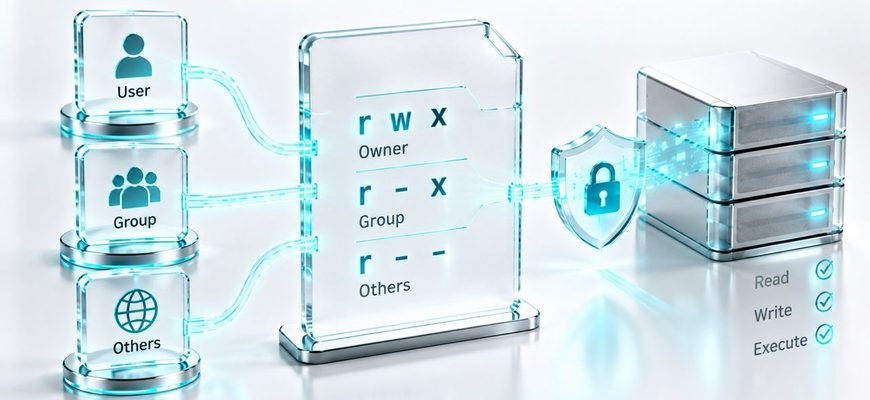
Linux does not let every user read, change, or run every file. Instead, each file and directory has an owner, a group, and a set of permissions that determine who can do what.
This is the system behind permission strings such as -rw-r--r--, commands such as chmod and chown, and many familiar errors such as Permission denied.
Once you understand the model, Linux permissions stop looking like cryptic symbols and start behaving like a simple access-control rule.
Traditional Linux file permissions define access for three classes: the owner, the group, and others.
Each class can receive read (r), write (w), and execute (x) permissions. chmod changes permission bits, while chown changes file ownership.
- How Linux decides whether a user can access a file.
- How to read strings such as
-rwxr-xr--. - What read, write, and execute mean for files and directories.
- How symbolic and numeric
chmodsyntax work. - What
chownchanges and why ownership matters. - How to inspect permissions safely on your own Linux system.
- 🔐 Why Linux Needs File Permissions
- 👤 Every File Has an Owner and a Group
- Owner
- Group
- Others
- 🧩 How to Read rwx Permissions
- 📖 What r, w, and x Mean for Files
- 📁 Permissions Mean Something Different on Directories
- 🔍 A Permission Example Step by Step
- Identify the owner
- Identify the group
- Split the permissions
- Interpret each class
- 🛠️ chmod Changes Permissions
- Symbolic chmod
- 🔢 Numeric chmod: Why 755 and 644 Work
- Read = 4
- Write = 2
- Execute = 1
- 👑 chown Changes Ownership
- 👥 Why Groups Matter
- 📁 File Permissions and Directory Permissions Work Together
- 🔍 How to Inspect Permissions Before Changing Anything
- 🧪 Mini Lab: Learn Permissions Safely
- 1. Create a practice file
- 2. Inspect its permissions
- 3. Give only the owner read and write permissions
- 4. Add read permission for the group
- 5. Remove the practice file
- ⚠️ Common Linux Permission Mistakes
- 🧠 A Simple Permission Troubleshooting Method
- Identify the current user
- Inspect ownership
- Read the permission bits
- Check parent directories
- Change only what is necessary
- What You Should Understand About Linux Permissions
🔐 Why Linux Needs File Permissions
A multi-user operating system needs boundaries.
An ordinary account should not automatically be able to modify every system configuration file. A web service should not need unrestricted access to every user’s home directory. A private SSH key should not be readable by unrelated accounts.
Linux solves much of this basic access-control problem by associating files and directories with ownership and permission information.
The traditional permission model is compact, fast, and used throughout Linux. More advanced access controls also exist, but understanding owner, group, and other permissions is the essential foundation.
👤 Every File Has an Owner and a Group
For permission purposes, Linux commonly divides access into three classes.
Owner
The user account recorded as the owner of the file or directory.
Group
The group associated with the object. Members of that group may receive the group permissions.
Others
Users who do not receive access through the owner or group class for that permission check.
You can see ownership and permission information with:
ls -lA simplified output line might look like this:
-rw-r----- 1 alice developers 2480 notes.txtThe important fields for this lesson are:
-rw-r-----   alice   developers   notes.txt
     │         │          │          │
     │         │          │          └── file name
     │         │          └───────────── group
     │         └──────────────────────── owner
     └────────────────────────────────── permissions
🧩 How to Read rwx Permissions
The permission string contains several pieces of information.
Consider:
-rwxr-xr--The first character identifies the object type. A regular file commonly begins with -, while a directory begins with d.
The remaining nine characters form three permission groups:
So -rwxr-xr-- means:
- The owner can read, write, and execute.
- The group can read and execute, but not write.
- Others can read, but cannot write or execute.
📖 What r, w, and x Mean for Files
| Permission | Symbol | Meaning for a Regular File |
|---|---|---|
| Read | r |
Allows the file’s contents to be read. |
| Write | w |
Allows the file’s contents to be modified. |
| Execute | x |
Allows the file to be executed when it is a suitable executable program or script. |
A missing permission is represented by a hyphen.
For example:
rw-means read and write are allowed, but execute is not.
📁 Permissions Mean Something Different on Directories
This is one of the most important concepts beginners often miss.
The same symbols are used for directories, but their practical meaning changes.
| Permission | Meaning for a Directory |
|---|---|
r — read |
Allows directory entries to be listed, subject to other access conditions. |
w — write |
Allows directory entries to be created or removed when the necessary directory permissions are present. |
x — execute/search |
Allows the directory to be traversed and names inside it to be accessed when other permission checks also permit the operation. |
For directories, x is best thought of as permission to traverse the directory. That is why a directory can behave unexpectedly if you look only at its read permission.
🔍 A Permission Example Step by Step
Suppose a file shows:
-rw-r----- 1 alice developers 2480 notes.txtIdentify the owner
The owner is alice.
Identify the group
The associated group is developers.
Split the permissions
The nine permission characters become rw-, r--, and ---.
Interpret each class
The owner can read and write. The group can read. Others receive no permissions from the traditional mode bits.
This approach works far better than trying to read all nine characters as one symbol.
🛠️ chmod Changes Permissions
The command chmod changes file mode bits.
There are two common ways to express the permissions you want: symbolic notation and numeric notation.
Symbolic chmod
Symbolic mode uses letters to describe who should receive or lose a permission.
| Symbol | Meaning |
|---|---|
u |
User / owner |
g |
Group |
o |
Others |
a |
All classes |
+ |
Add permission |
- |
Remove permission |
= |
Set the selected class to the specified permissions |
For example, this adds execute permission for the owner:
chmod u+x script.shThis removes write permission from the group:
chmod g-w notes.txtAnd this gives others read permission:
chmod o+r notes.txt🔢 Numeric chmod: Why 755 and 644 Work
Linux permissions are also commonly expressed using octal numbers.
Each basic permission has a value:
Read = 4
r contributes the value 4.
Write = 2
w contributes the value 2.
Execute = 1
x contributes the value 1.
Add the values within each permission class.
| Number | Permissions | Calculation |
|---|---|---|
| 7 | rwx |
4 + 2 + 1 |
| 6 | rw- |
4 + 2 |
| 5 | r-x |
4 + 1 |
| 4 | r-- |
4 |
| 0 | --- |
No permissions |
A mode such as:
chmod 755 script.shmeans:
7   5   5
│   │   │
│   │   └── others: r-x
│   └────── group:  r-x
└────────── owner:  rwx
So 755 corresponds to:
rwxr-xr-xSimilarly:
chmod 644 notes.txtcorresponds to:
rw-r--r--Do not treat 777 as a universal fix for permission errors. It grants read, write, and execute permissions to owner, group, and others. That is usually much broader access than a file or directory actually needs.
👑 chown Changes Ownership
chmod changes permissions. chown changes ownership.
This distinction matters:
chmodchownFor example:
chown alice notes.txtchanges the file owner to alice, assuming the command is run with sufficient privileges.
You can specify both user and group:
chown alice:developers notes.txtThis sets the owner to alice and the group to developers.
Changing file ownership is a privileged operation. On a typical system, an ordinary user cannot arbitrarily transfer file ownership to another account. Avoid using elevated privileges until you understand exactly which object you are changing and why.
👥 Why Groups Matter
Groups let multiple users receive access through one permission class.
Imagine three developers who need to collaborate on the same project files. Instead of granting access individually through basic mode bits, the files can belong to a shared group and receive appropriate group permissions.
If a project file belongs to the developers group and has group write permission, qualifying members of that group can work with the file according to the directory permissions and other access-control rules in effect.
You can inspect your current user and group memberships with:
idOr list group names associated with your current account using:
groups📁 File Permissions and Directory Permissions Work Together
A common troubleshooting mistake is to examine only the file itself.
Suppose a file has readable permissions, but you cannot reach it because one of its parent directories does not permit traversal for your account. The file’s own read bit does not remove the need to traverse the path leading to it.
Conceptually:
Linux may need to check permissions at multiple points along that path.
When a file produces Permission denied, do not automatically change the file to 777. First ask: Who is the current user? Who owns the file? Which group applies? What are the file permissions? Can the user traverse the parent directories?
🔍 How to Inspect Permissions Before Changing Anything
A good administrator investigates before modifying permissions.
Start with:
ls -l filenameFor a directory itself, use:
ls -ld directoryThe -d option matters here because it asks ls to show information about the directory entry itself rather than listing its contents.
You can also inspect detailed metadata with:
stat filenameThe exact formatting varies by implementation and system, but stat provides useful ownership, mode, and filesystem metadata.
🧪 Mini Lab: Learn Permissions Safely
Goal: Observe permission changes using a disposable file in your own home directory.
1. Create a practice file
The following command creates an empty file named permission-lab.txt in your current directory.
touch permission-lab.txt2. Inspect its permissions
ls -l permission-lab.txtWhat to observe: Note the owner, group, and permission string. The exact initial permissions depend on your environment and the process umask.
3. Give only the owner read and write permissions
This command sets the traditional permission bits to 600:
chmod 600 permission-lab.txtInspect the result:
ls -l permission-lab.txtWhat to observe: The permission portion should represent rw-------: read and write for the owner, with no group or other permissions.
4. Add read permission for the group
chmod g+r permission-lab.txtCheck again:
ls -l permission-lab.txtHow to interpret it: You changed only the group read bit while leaving the other selected permissions unchanged.
5. Remove the practice file
When finished, delete only the disposable file created for this lab:
rm permission-lab.txt⚠️ Common Linux Permission Mistakes
This grants every basic permission to all three classes. It may hide the underlying ownership or configuration problem while unnecessarily broadening access.
chmod changes permission bits. chown changes the owner and, when requested, the associated group. They solve different problems.
For a regular executable file, x permits execution. For a directory, x controls traversal or search access through that directory.
Access can also depend on permissions of the directories leading to that file. A readable file may still be unreachable if the path cannot be traversed.
These modes are common in certain contexts, but permissions should match the actual access requirements of the file or directory rather than being applied mechanically.
🧠 A Simple Permission Troubleshooting Method
When Linux denies access, work through the problem in a fixed order instead of changing random permissions.
Identify the current user
Use id to understand which user and groups are involved.
Inspect ownership
Check which user and group own the target file or directory.
Read the permission bits
Determine whether the owner, group, or other permission class applies to the operation.
Check parent directories
Make sure the account can traverse the path to the object.
Change only what is necessary
If a change is genuinely required, prefer the smallest ownership or permission adjustment that solves the intended access problem.
The goal of permission management is not to make an error disappear. The goal is to give the correct identity exactly the access it needs while avoiding unnecessary access for everyone else.
What You Should Understand About Linux Permissions
Linux permissions combine two ideas: identity and allowed actions.
The identity side asks which user owns the object, which group is associated with it, and which account is trying to access it.
The permission side asks whether that relevant class has read, write, or execute permission for the requested operation.
Once these two parts are separated mentally, permission strings become much easier to decode:
chmod changes the allowed actions. chown changes ownership. Commands such as ls -l, ls -ld, id, and stat help you understand the existing state before changing anything.
- In the permission string
-rwxr-xr--, what can the owner, group, and others do? - Why does execute permission mean something different for a directory than for a regular file?
- What is the conceptual difference between
chmodandchown? - What permissions does numeric mode
640represent? - Why might a readable file still produce a permission error when you try to access it?
- Why is
chmod 777usually a poor first response to a permission problem?
🎓 Check Your Answers
- The owner has
rwx, so the owner can read, write, and execute. The group hasr-x, so it can read and execute but not write. Others haver--, so they can read but cannot write or execute. - On a regular file,
xpermits the file to be executed when it contains a suitable executable program or script. On a directory,xprovides traversal or search access, allowing names inside the directory to be reached when the other permission requirements are satisfied. chmodchanges file mode permissions such as read, write, and execute.chownchanges the recorded owner and optionally the associated group. Permissions and ownership are related but separate pieces of metadata.640meansrw-r-----. The owner receives read and write permissions, the group receives read permission, and others receive no basic permissions.- Access depends on more than the final file’s read bit. Linux may also require traversal permission on each relevant parent directory, so a user can be blocked earlier in the path even when the target file itself appears readable.
777grants read, write, and execute permissions to owner, group, and others. That can expose the object far more broadly than necessary and can hide the real issue, such as incorrect ownership, group membership, or directory permissions.
Linux permissions answer two questions: who is requesting access, and what is that identity allowed to do? The traditional model separates access into owner, group, and others, with read, write, and execute permissions for each.
Remember the operational distinction: chmod changes permissions; chown changes ownership. Before changing either one, inspect the user, group, file, and parent directories so you solve the real access problem instead of simply making permissions broader.