A server can have a valid IP address, a working route, correct DNS resolution, and an application listening on a TCP port — yet a connection can still be blocked. One reason is the firewall.
A Linux firewall applies rules to network traffic. Those rules can examine properties such as direction, protocol, source or destination address, port, interface, and connection state before deciding what should happen to the traffic.
Understanding this model is more useful than memorizing a few firewall commands. Once you know what the firewall is actually evaluating, tools such as nftables, iptables, UFW, and firewalld become much easier to reason about.
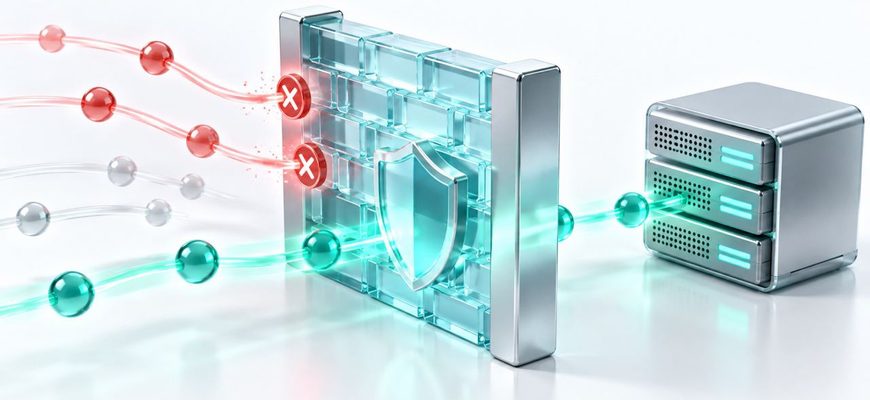
A Linux firewall filters network traffic according to rules. A rule can match characteristics of a packet or connection — for example, TCP traffic arriving on a network interface for port 22 — and then specify an action such as accepting or dropping it.
The firewall is not the same thing as a listening service. A service may be listening on a port while firewall policy prevents remote clients from reaching it.
- Where a firewall fits into normal server networking.
- What firewall rules actually match.
- The difference between allowing a port and having a service listen on it.
- Why rule order and default policy matter.
- How nftables, iptables, UFW, and firewalld relate to the underlying concept.
- How to inspect firewall state without changing it.
- 🧱 What Is a Firewall?
- 🔍 What Can a Firewall Rule Look At?
- Addresses
- Protocol & Port
- Interface & Direction
- 📥 Incoming, Outgoing, and Forwarded Traffic
- 🔌 A Firewall Port Is Not the Same as a Listening Port
- 🧭 How a Firewall Decision Happens
- Traffic reaches the Linux networking stack
- The system identifies the traffic path
- Relevant rules are evaluated
- A rule determines what happens next
- 🔄 Connection State Changes the Picture
- 📚 Why Rule Order and Default Policy Matter
- 🧰 nftables, iptables, UFW, and firewalld
- 🧪 Mini Lab: Inspect Without Changing the Firewall
- 1. Inspect listening sockets
- 2. Check for common firewall tools
- 3. Inspect nftables if it is the active framework you administer
- 4. If the server is managed with UFW
- 5. Compare sockets with firewall policy
- 🔍 A Better Troubleshooting Model
- ⚠️ Common Firewall Mistakes
- 🧠 What You Should Understand Before Configuring Rules
🧱 What Is a Firewall?
A firewall is a traffic-control mechanism. It applies policy to network traffic and decides whether matching traffic should be permitted, rejected, dropped, or otherwise processed according to the configured rules.
On a Linux server, packet filtering is implemented inside the kernel. Administration tools provide ways to define and manage the rules that the kernel uses.
This distinction matters because names such as nftables, iptables, UFW, and firewalld refer to different parts of the firewall-management landscape. They are not four separate conceptual reasons that traffic gets filtered.
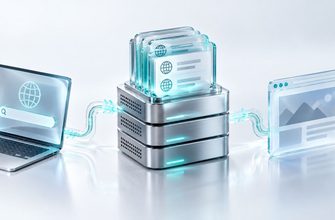
That simplified flow is useful for incoming traffic destined for a local service. It explains an important troubleshooting principle: reaching the machine and reaching the application are not always the same thing.
🔍 What Can a Firewall Rule Look At?
A useful mental model is to think of each rule as having two parts:
Match conditions → action
The match conditions describe the traffic the rule applies to. The action describes what should happen when those conditions match.
Addresses
A rule can distinguish traffic by source or destination IP address or network.
Protocol & Port
Rules can distinguish protocols such as TCP and UDP and, where applicable, their ports.
Interface & Direction
Policy can depend on where traffic enters, leaves, or is being forwarded.
Modern firewall rules can evaluate much more than these examples, but these concepts are enough to understand most beginner server configurations.
For example, an administrator might conceptually express a policy like:
incoming + TCP + destination port 22 → allowThat is a conceptual rule, not a command to paste into a terminal. The exact syntax depends on the firewall framework and management tool being used.
📥 Incoming, Outgoing, and Forwarded Traffic
Not all traffic has the same relationship to the server.
| Traffic type | Meaning | Example |
|---|---|---|
| Incoming | Traffic whose destination is this Linux host. | A remote administrator connecting to the server’s SSH service. |
| Outgoing | Traffic generated locally and sent toward another host. | The server contacting a DNS resolver or software repository. |
| Forwarded | Traffic passing through the Linux host rather than terminating on it. | A Linux router forwarding packets between networks. |
A basic public server is often discussed mainly in terms of incoming connections, but Linux can also act as a router, gateway, container host, or virtualization host. In those environments, forwarding becomes especially important.
🔌 A Firewall Port Is Not the Same as a Listening Port
This distinction prevents a great deal of confusion.
A listening socket means a local application is prepared to receive matching traffic. A firewall rule controls whether traffic is permitted through the relevant filtering policy.
These are separate conditions.
| Application | Firewall | Likely result |
|---|---|---|
| Listening | Allows traffic | The connection can proceed to the service, assuming the rest of the network path works. |
| Listening | Blocks traffic | The application exists, but matching traffic is stopped by firewall policy. |
| Not listening | Allows traffic | The firewall permits the traffic, but no application is waiting on that socket. |
| Not listening | Blocks traffic | Firewall policy blocks the traffic and no local service is available anyway. |
“The port is open” is often too vague for troubleshooting. Ask two separate questions: Is an application listening? and Does firewall policy allow the traffic?
🧭 How a Firewall Decision Happens
The exact processing path depends on the firewall configuration, but a simplified model helps explain the logic.
Traffic reaches the Linux networking stack
A packet arrives from a network interface or is generated locally.
The system identifies the traffic path
The packet may be destined for the local host, leaving the host, or being forwarded through it.
Relevant rules are evaluated
The configured rules can compare properties such as addresses, protocol, ports, interfaces, and connection state.
A rule determines what happens next
Depending on the ruleset, matching traffic may be accepted, dropped, rejected, logged, or processed in another defined way.
This is why firewall troubleshooting requires understanding the whole ruleset rather than searching for one line containing a port number.
🔄 Connection State Changes the Picture
Many practical firewall configurations are stateful. Instead of treating every packet as completely unrelated to every other packet, the system can track connection information and distinguish traffic associated with an existing flow from traffic attempting to begin a new one.
Imagine that the server is allowed to initiate an outbound connection to a software repository. The response packets coming back belong to that communication. A state-aware ruleset can recognize that relationship rather than requiring a broad rule that permits arbitrary new inbound connections.
This produces a more useful policy model:
allow traffic associated with established communication
allow selected new inbound services
block other unsolicited inbound traffic
Again, this is conceptual policy rather than firewall command syntax.
📚 Why Rule Order and Default Policy Matter
A firewall is not merely a list of port numbers. Rules belong to a structured ruleset, and their evaluation semantics matter.
In rulesets where processing order affects the result, a broad rule encountered earlier can change what happens before a later, more specific rule would otherwise apply. This is one reason blindly adding rules can produce unexpected behavior.
The other major concept is the policy for traffic that does not receive an explicit permit.
A common security approach for exposed services is to permit the traffic that is actually required and deny or drop unwanted unsolicited traffic. But the correct policy depends on the server’s role, management requirements, network design, and recovery options.
Changing firewall rules on a remote server can disconnect your SSH session and prevent you from reconnecting. Before applying restrictive rules, confirm how administrative access is permitted and make sure you have a recovery path such as the provider’s console or equivalent out-of-band access.
🧰 nftables, iptables, UFW, and firewalld
The names used around Linux firewalls can be confusing because they operate at different abstraction levels and have changed over Linux’s history.
| Name | Role | Beginner mental model |
|---|---|---|
| nftables | Modern Linux packet-filtering framework configured through the nftables userspace tooling. | A direct framework for defining Linux firewall rulesets. |
| iptables | Long-established command-line interface and rule model for Linux packet filtering; modern distributions may provide compatibility implementations backed by nftables. | An older and still commonly encountered firewall interface. |
| UFW | A higher-level firewall management tool designed to simplify common firewall configuration. | A simpler administrative interface for common allow/deny policies. |
| firewalld | A firewall management service that provides higher-level concepts and dynamic rule management. | A management layer commonly found on several Linux distributions. |
The important lesson is not to mix commands from several firewall managers without understanding which system is controlling the active ruleset.
Learn the policy before the syntax. “Allow SSH from this management network” is a firewall policy decision. The nftables, UFW, or firewalld command used to express it is an implementation detail that can be learned afterward.
🧪 Mini Lab: Inspect Without Changing the Firewall
Goal: identify listening sockets and discover which firewall management tools are available without modifying the ruleset.
1. Inspect listening sockets
ss -lntupDepending on your permissions, some process information may not be visible. Focus first on the local addresses, protocols, and ports.
A listening socket tells you that an application is waiting for traffic. It does not prove that a remote firewall path permits access to it.
2. Check for common firewall tools
command -v nft
command -v iptables
command -v ufw
command -v firewall-cmd
A printed path means that command exists in your current environment. It does not by itself prove that the tool owns or actively manages the server’s firewall policy.
3. Inspect nftables if it is the active framework you administer
sudo nft list rulesetThis displays the nftables ruleset visible to your account. Reading the ruleset does not itself change firewall policy.
4. If the server is managed with UFW
sudo ufw status verboseLook for whether UFW is active and, if so, what policy and rules it reports.
5. Compare sockets with firewall policy
Choose one service you recognize. Ask: Is the application listening? On which address? Which protocol and port does it use? Does the firewall configuration contain policy relevant to that traffic?
The goal is observation, not rule modification.
🔍 A Better Troubleshooting Model
When a remote service cannot be reached, do not immediately assume “the firewall is broken.” Work through the network path in layers.
If the expected interface or address is missing, changing firewall policy may be irrelevant. If the service is not listening, allowing its port through the firewall will not make the application start. If the local firewall allows the traffic, another network firewall or provider-level security control may still exist elsewhere in the path.
Each layer answers a different question.
⚠️ Common Firewall Mistakes
A listening socket proves that a local application is waiting. Firewall policy and the rest of the network path can still prevent a remote connection.
A firewall rule only affects traffic policy. It does not launch the application that should listen on that port.
Routing, DNS, application binding, service state, provider firewalls, and other network controls can produce similar symptoms. Diagnose the path instead of guessing.
A mistake in remote firewall policy can lock you out. Verify the management rule and recovery path before changing access controls.
They represent different interfaces or management layers. First determine how the host’s firewall is actually managed before making changes.
🧠 What You Should Understand Before Configuring Rules
You do not need to memorize firewall syntax yet. You need a reliable model.
First, identify the traffic: Is it incoming, outgoing, or forwarded? Which protocol is involved? If TCP or UDP is involved, which relevant source or destination port is being used? Which addresses and interfaces matter?
Second, separate application state from network policy. A service listening on TCP port 443 and a firewall permitting TCP port 443 are different facts.
Third, remember that a server can have several filtering layers. A VPS provider may have a network firewall outside the virtual machine while Linux has its own host firewall inside it. Changing one does not automatically change the other.
Finally, inspect before modifying. Firewall mistakes can affect the very connection you are using to administer the server.
- What are the two conceptual parts of a firewall rule?
- Why does a listening TCP socket not prove that the service is remotely reachable?
- What is the difference between incoming and forwarded traffic?
- Why is connection state useful in a firewall ruleset?
- Does allowing TCP port 22 in a firewall start an SSH server?
- Why should you be especially careful when changing firewall rules over SSH?
🎓 Check Your Answers
- A firewall rule conceptually combines match conditions with an action. The conditions identify the traffic the rule applies to, while the action determines what the firewall should do with matching traffic.
- A listening socket describes the local application state. Firewall rules, routing, provider-level controls, and other parts of the network path can still prevent a remote client from reaching that socket.
- Incoming traffic is destined for the Linux host itself. Forwarded traffic is passing through the Linux host toward another destination, which is common when Linux acts as a router or gateway.
- Connection tracking lets firewall policy recognize traffic associated with existing communication. This makes it possible to permit legitimate response traffic without broadly allowing arbitrary new inbound connections.
- No. A firewall rule permitting TCP port 22 only allows matching traffic through that filtering policy. An SSH service must separately be installed, running, and listening on an appropriate socket.
- Your SSH connection depends on network access to the server. A restrictive or incorrect firewall change can block the management traffic and prevent you from reconnecting, so the access rule and recovery method should be verified first.
A Linux firewall is a policy engine for network traffic. Rules identify traffic using properties such as direction, protocol, addresses, ports, interfaces, and connection state, then determine how matching traffic should be handled.
Keep the layers separate in your mental model: the network delivers traffic, the firewall filters it, a socket receives permitted traffic, and the application provides the service. Once that model is clear, learning nftables, UFW, firewalld, or other firewall-management syntax becomes much easier.