How to edit Linux configuration files safely starts with one simple habit: never make a change you don’t understand or can’t undo.
You’re connected to your first Linux server. The software is installed, everything seems to be working, and the next instruction says: “Open the configuration file and change the following setting.”
That’s where things become less obvious. Which file should you open? Do you need administrator permissions? What if you accidentally remove an important line? And how do you know the application will still work after saving?
In this guide, you’ll learn how Linux configuration files work, how to edit them using nano and sudoedit, and how to back up, validate, and restore settings. We’ll start with a safe practice exercise before looking at a real server application.
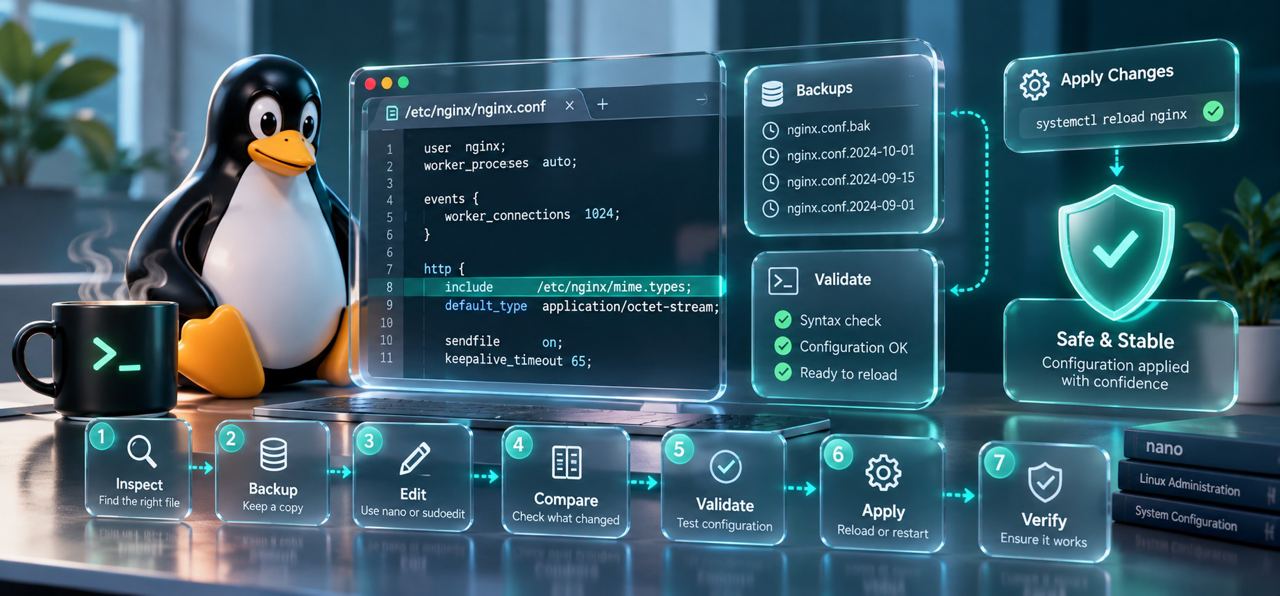
To edit a Linux configuration file safely,
inspect it with cat or
less, create a backup using
cp, edit it with
nano or sudoedit,
compare changes with diff,
and validate the configuration before
applying it. After reloading or restarting
the affected service, verify that it
behaves as expected.
- 01 What Is a Linux Configuration File?
- Readable settings
- Different formats
- Important consequences
- A simple configuration example
- 02 Where Are Linux Configuration Files Stored?
- 03 How to Edit Linux Configuration Files in 7 Safe Steps
- 04 Read a Configuration File Before Editing It
- Read a short file with cat
- Browse longer files with less
- Find a specific setting
- 05 How to Edit Linux Configuration Files with nano
- Open a configuration file
- Essential nano shortcuts
- 06 Permissions: When Should You Use sudoedit?
- Check file ownership
- 07 Back Up Configuration Files and Review Changes
- Create a backup
- Compare the original and edited files
- Practice: How to Edit Linux Configuration Files Safely
- Create a practice directory
- Create a sample configuration file
- Create a backup
- Edit one setting
- Compare your changes
- Verify the edited setting
- Restore the original version
- 08 Editing a Real Linux Service Configuration
- Inspect the current configuration
- Save a backup
- Make an authorized edit
- Review the difference
- Validate the configuration
- Reload and verify
- Restore the previous configuration
- 09 Reload vs. Restart: What’s the Difference?
- 10 Common Linux Configuration Editing Mistakes
- Be especially careful with SSH configuration
- 11 Frequently Asked Questions
- 12 Linux Configuration Editing Safety Checklist
- A Safe Configuration Change Is One You Can Undo
- Continue Learning Linux Administration
- Technical References
What Is a Linux Configuration File?
A configuration file tells a program how it should behave.
The program already contains the code needed to do its job. The configuration provides the settings that determine exactly how it operates.
For example, a web server knows how to handle HTTP requests. Its configuration determines which websites to serve, which ports to listen on, and how incoming connections should be handled.
Readable settings
Many Linux applications store configuration in text files that you can inspect directly from the terminal.
Different formats
Each application has its own configuration rules. There is no single syntax shared by every Linux service.
Important consequences
A wrong setting may change application behavior or prevent a service from starting correctly.
A simple configuration example
Imagine a small application using the following settings:
# Application settings
mode=development
timeout_seconds=30
logging=enabled
Here, timeout_seconds=30
represents a timeout value. If the
application recognizes this setting,
changing it to 45 would
adjust the timeout.
Real configuration files may contain hundreds of settings, nested sections, comments, and references to additional configuration files.
This example uses a fictional application. Linux does not have one universal configuration format. Applications may use INI, YAML, JSON, TOML, or their own syntax.
Where Are Linux Configuration Files Stored?
Many system-wide configuration files
are stored in /etc.
This directory contains settings for operating system components, services, and installed applications. However, not every configuration file lives there.
| Location | Purpose | Example |
|---|---|---|
/etc/ |
System-wide configuration | Network and service settings |
/etc/nginx/ |
Nginx web server | nginx.conf |
/etc/ssh/ |
OpenSSH configuration | sshd_config |
~/.config/ |
User-specific application settings | Application directories |
/etc/systemd/system/ |
Local systemd unit files and overrides | Service definitions and drop-ins |
These are common locations, not a guarantee that every file exists on every Linux distribution.
A fresh VPS may not have Nginx installed,
for example. And some applications store
their configuration outside
/etc.
When you’re unsure which file to edit, check the application’s documentation instead of guessing.
How to Edit Linux Configuration Files in 7 Safe Steps
The safest way to make configuration changes is to follow the same basic procedure every time.
You don’t need to memorize every Linux command. You need a process that makes your changes predictable, testable, and reversible.
| Step | Action | Purpose |
|---|---|---|
| 1 | Inspect the file | Confirm you’re editing the correct configuration. |
| 2 | Understand the setting | Know what the change will affect. |
| 3 | Create a backup | Preserve the original configuration. |
| 4 | Edit carefully | Make one controlled change. |
| 5 | Compare versions | Identify accidental modifications. |
| 6 | Validate | Check whether the application accepts the configuration. |
| 7 | Apply and verify | Confirm the service works as expected. |
Read a Configuration File Before Editing It
Before opening a text editor, inspect the file you’re planning to change.
You may discover that the setting already exists, has been disabled by a comment, or is defined in another configuration file.
Read a short file with cat
cat /etc/hostname
The cat command prints
the contents of the file directly
in your terminal.
Browse longer files with less
less /etc/hosts
The less utility lets
you scroll through a file without
modifying it.
Press / to search,
n to move to the next
match, and q to quit.
Find a specific setting
grep -n 'localhost' /etc/hosts
The -n option displays
matching line numbers.
This is particularly helpful when working with large configuration files containing hundreds of lines.
How to Edit Linux Configuration Files with nano
Nano is a terminal-based text editor. It’s a sensible starting point for beginners because you can type immediately after opening a file.
Its most useful keyboard shortcuts are displayed at the bottom of the screen.
Open a configuration file
nano myfile.confIf the file exists, nano opens it. If it doesn’t exist, nano can create it when you save, provided you have permission to write in that location.
Essential nano shortcuts
| Action | Shortcut | What happens |
|---|---|---|
| Save | Ctrl + O |
Write the file and confirm its name. |
| Exit | Ctrl + X |
Close nano, prompting if changes are unsaved. |
| Search | Ctrl + W |
Find text inside the file. |
| Cut line | Ctrl + K |
Cut the current line. |
| Paste | Ctrl + U |
Paste text from nano’s cut buffer. |
Nano uses the ^ symbol
to represent the Control key.
For example, ^O
means Ctrl + O.
Change one setting at a time whenever possible. Smaller changes are easier to understand, review, test, and reverse.
Permissions: When Should You Use sudoedit?
Linux prevents ordinary users from modifying protected system configuration files without authorization.
This is an important security feature, not an inconvenience that should be bypassed.
Check file ownership
ls -l /etc/hostsThe output displays the file’s owner, group, and permission bits.
If you need to edit a protected
file and your account is authorized,
sudoedit is often
a good choice.
SUDO_EDITOR=nano sudoedit /path/to/config.confReplace the example path with the file you need to edit.
Unlike running an entire editor with root privileges, sudoedit normally lets your regular account edit a temporary copy.
After you finish editing, sudo installs the updated contents at the protected location, subject to the applicable permissions and policy.
Don’t use chmod 777
or change file ownership just
to make a protected configuration
writable. Determine which account
is supposed to manage the file
and use an authorized method.
Back Up Configuration Files and Review Changes
A backup gives you a known version to return to if something goes wrong.
Without one, fixing a configuration mistake can become a guessing game: which settings changed, and what were their original values?
Create a backup
For a normal file you own:
cp -p myfile.conf myfile.conf.bak
The -p option attempts
to preserve file attributes such
as permissions and timestamps.
For a protected Nginx configuration, an administrator might use:
sudo cp -a -- /etc/nginx/nginx.conf /etc/nginx/nginx.conf.bak
This example assumes Nginx is installed.
The -a option preserves
file attributes and is useful when
backing up system configuration.
The command will overwrite an existing
file named nginx.conf.bak.
On a production system, consider using
a dated backup filename and keeping
track of which version was known to work.
Configuration files sometimes contain credentials or secrets. Their backups need appropriate access restrictions too. Never place sensitive backups inside a publicly accessible website directory.
Compare the original and edited files
The diff utility shows
exactly what changed between
two versions.
diff -u myfile.conf.bak myfile.conf
Removed lines begin with
-, while added lines
begin with +.
-timeout_seconds=30
+timeout_seconds=45
This is the kind of change you want to see: small, intentional, and easy to explain.
Note that diff
normally returns exit status
1 when files differ.
That does not necessarily mean
the command failed.
Practice: How to Edit Linux Configuration Files Safely
Now it’s time to practice. We’ll create a simple configuration file in your home directory, edit one setting, compare the results, and restore the original version.
This exercise does not modify any real Linux service and does not require root access.
You’ll need a Linux terminal,
nano, and a regular user account.
This lab creates a directory
called sa-config-lab
inside your home directory.
Create a practice directory
Keep the exercise separate from your other files.
mkdir ~/sa-config-lab && cd ~/sa-config-labThis creates a new directory and enters it. If the directory already exists, the command stops rather than silently reusing an existing workspace.
Create a sample configuration file
Paste the following command into your terminal:
cat > app.conf <<'EOF'
mode=development
timeout_seconds=30
logging=enabled
EOF
This creates a text file
named app.conf.
The command overwrites an
existing file with that name,
so use the new practice
directory from Step 1.
Check its contents:
cat app.confCreate a backup
Before making any changes, save the original file.
cp -p app.conf app.conf.bak
You now have two files:
app.conf and
app.conf.bak.
We’ll edit only the first one.
Edit one setting
Open the working file using nano:
nano app.confFind this line:
timeout_seconds=30Change it to:
timeout_seconds=45
Press Ctrl + O
to save, confirm the filename
with Enter, and press
Ctrl + X to exit.
Compare your changes
Compare the working file with the backup:
diff -u app.conf.bak app.conf
You should see the timeout
value change from
30 to
45.
The other settings should remain unchanged.
Verify the edited setting
Search for the timeout line:
grep -n '^timeout_seconds=' app.confYou should see:
2:timeout_seconds=45This confirms the expected setting is present.
It is not a full syntax check because our example application is fictional and has no configuration parser.
Restore the original version
Now practice undoing the change.
cp -p app.conf.bak app.confCompare both files again:
diff -u app.conf.bak app.confIf the command prints nothing, the files have identical contents.
You’ve completed a full configuration editing cycle without modifying any real system services.
Editing a Real Linux Service Configuration
The practice file was intentionally harmless. A real service requires another essential step: validating the configuration before applying it.
Let’s use Nginx as an example. Nginx is commonly used to serve websites and handle web traffic on Linux servers.
The commands below assume Nginx is already installed and managed by systemd. They illustrate the procedure rather than a specific configuration change. Practice on a test server before modifying a production website.
Inspect the current configuration
sudo less /etc/nginx/nginx.confLook for configuration directives and included files. Nginx often loads settings from several configuration locations.
Save a backup
sudo cp -a -- /etc/nginx/nginx.conf /etc/nginx/nginx.conf.bakBack up any included files that you’re planning to change as well.
Make an authorized edit
SUDO_EDITOR=nano sudoedit /etc/nginx/nginx.confMake only the change you’ve already planned and understood.
Review the difference
sudo diff -u /etc/nginx/nginx.conf.bak /etc/nginx/nginx.confCheck that only the intended lines changed.
Validate the configuration
sudo nginx -t
The nginx -t command
checks configuration syntax
and attempts to open referenced
files.
A successful test means those checks passed. It does not guarantee that every setting is logically correct for your environment.
Do not reload the service. Read the reported error, identify the affected file and setting, and correct the problem first.
Reload and verify
If validation succeeds and the change supports a reload, apply the new configuration:
sudo systemctl reload nginxThen check the service status and recent logs:
systemctl status nginx --no-pager

sudo journalctl -u nginx -n 30 --no-pager
Finally, test the website or endpoint affected by your change.
A service may be running while still behaving incorrectly. That’s why functional verification matters as much as syntax checking.
Restore the previous configuration
If the change causes a problem and the backup is known to be the correct previous version, restore the main configuration:
sudo cp -a -- /etc/nginx/nginx.conf.bak /etc/nginx/nginx.conf

sudo nginx -t
If validation succeeds, apply the restored configuration using the appropriate service procedure and verify the result.
Remember that restoring only
nginx.conf may not
restore the complete configuration
if you also changed included files.
Reload vs. Restart: What’s the Difference?
Saving a configuration file doesn’t necessarily make its new settings active.
Some applications support configuration reloads. Others require a full restart.
| Command | What it does | Typical use |
|---|---|---|
systemctl reload |
Requests that a service reload its configuration, if supported. | Applying supported settings without a complete restart. |
systemctl restart |
Stops and starts the service. | Changes requiring a full restart. |
systemctl daemon-reload |
Makes systemd reread unit definitions. | Changes to systemd unit files or drop-ins. |
These commands are not interchangeable.
For example,
systemctl daemon-reload
is not a general substitute for
reloading an application’s
own configuration.
Always check how the particular service applies its settings.
Common Linux Configuration Editing Mistakes
Understanding how to edit Linux configuration files also means knowing what to investigate when a change doesn’t work.
| Problem | Possible cause | What to check |
|---|---|---|
| Permission denied | Your account cannot write to the file. | File ownership, permissions, and authorized privileges. |
| Syntax error | The application cannot parse the configuration. | The reported file, line, and configuration syntax. |
| Changes have no effect | The service may not have reloaded or may use another file. | Active configuration paths, includes, and reload procedure. |
| Settings revert unexpectedly | Automation may be managing the configuration. | Deployment tools and configuration management systems. |
| Service behaves incorrectly | The configuration may be valid but logically wrong. | Application behavior, logs, and the previous configuration. |
Be especially careful with SSH configuration
If you administer a remote VPS through SSH, an incorrect server configuration can prevent new connections.
Before changing SSH settings, make sure you have an alternative recovery method, such as your hosting provider’s console.
Keep your current SSH session open while testing the change.
On systems with the OpenSSH server installed, you can normally check its configuration syntax using:
sudo sshd -tA successful syntax check does not guarantee that your authentication or access policy will behave as intended.
After applying the change, confirm that a new SSH connection works before closing the original session.
Frequently Asked Questions
How do I edit a Linux configuration file?
Locate the correct file, inspect its contents, create a backup, and open it using nano or another text editor. After editing, compare your changes, validate the configuration, and verify that the application works correctly.
Is nano easier than vim for beginners?
Nano is generally easier to learn because it allows immediate text editing and displays its main keyboard shortcuts. Vim is powerful, but it isn’t necessary for your first configuration changes.
Should I always use sudo?
No. Use normal permissions for files you own. Elevated privileges are appropriate only when required and authorized. For protected files, sudoedit is often preferable to running an entire text editor as root.
Why didn’t my configuration change take effect?
The application may need to reload its configuration, another file may override the setting, or the program may be reading a different configuration file. Check the application’s documentation and active settings.
Can I restore a configuration after making a mistake?
Usually, if you have a suitable backup or version history. Restore the known-good files, validate the restored configuration, apply it using the application’s documented procedure, and verify the result.
Linux Configuration Editing Safety Checklist
Before modifying a configuration on a working Linux server, check the following points.
A Safe Configuration Change Is One You Can Undo
Learning how to edit Linux configuration files safely is not about memorizing hundreds of commands.
It’s about developing a reliable working habit: understand the setting, preserve the original, make a small change, check the result, and keep a recovery path available.
Start with the practice lab. Once you’re comfortable editing, comparing, and restoring a simple file, you’ll be better prepared to manage real Linux services.
Continue Learning Linux Administration
Configuration editing connects several fundamental Linux skills. These lessons explain the next pieces.
Technical References
The commands and service behavior covered in this tutorial are documented in the following technical references.